
 English
 English (US)
 English (AU)
 English (NZ)
 English (SA)
 Français
 Français (CA)
 Italiano
 Deutsch
 Español
 Español (LatAm)
 Nederlands
 Português
 Português (BR)
 Polski
 العربية
 עברית
 Svenska
 Dansk
 Suomi
 Norsk
 Български
 Ελληνικά
 Lietuvių
 Română
 Čeština
 Magyar
 Türkçe
 日本語
On 12 October 2026, France’s national computer emergency response team, CERT-FR, issued an alert saying it was aware of numerous compromises of the remote controllers that run commercial refrigeration installations. Three weeks later the problem was European. A joint statement from ENISA, the European Commission, Europol’s European Cybercrime Centre and the EU network of national incident response teams said that since 11 October, commercial refrigeration systems had been hit in a number of EU member states, with a new wave of incidents on 1–2 November.
Investigations are still running. But the advisories published so far already say enough for chilled and frozen food businesses to act on before the Christmas peak.
What happened in the UK
The second wave reached Britain. Launching the National Cyber Security Centre’s annual review on 3 November, its chief executive Richard Horne said: “Our resulting exposure as a society is huge and increasingly exploited in cyber attacks as we are seeing in the disruption of refrigeration units across Europe.”
The NCSC described the national impact as minimal, according to The Record’s report of the launch. The Association of Independent Meat Suppliers told the same publication that three of its members had been affected and that none had lost meat, adding that the incident “must act as a reminder to all in the food industry, at whatever point in the supply chain they are, that their businesses may be seen by some as targets.” A British fruit and vegetable wholesaler described physically unplugging a fridge from the internet after watching it being remotely put into defrost mode.
Most of these businesses avoided losses because someone noticed in time. That should not be a matter of luck.
The problem with trusting the controller
On 5 November, five US agencies, including the Cybersecurity and Infrastructure Security Agency (CISA) and the FBI, published a joint fact sheet. It says attackers may exploit unpatched or internet-accessible controllers “to remotely alter settings and force units into continuous heating and defrost cycles”. Among the possible effects it lists is “Loss of visibility into current temperatures (a denial-of-view condition).”
That phrase is the heart of the problem. In many sites, one controller does several jobs: it runs the refrigeration, shows the temperature, raises the alarm and keeps the log. If an attacker controls that box, they can control what you see as well as what the fridge does. A temperature screen that reads normal while the load warms up is worse than no screen at all, because it stops anyone from checking.
The same fact sheet notes that these controllers are widely used, “including in refrigerated transport services”, for remote temperature monitoring, continuous logging and defrost management. The incidents reported so far have been at fixed sites such as supermarkets, cold stores and processors, and none of the advisories describes a vehicle being compromised. But the design question is the same whether the cold space is a store room or a trailer.
An independent second record
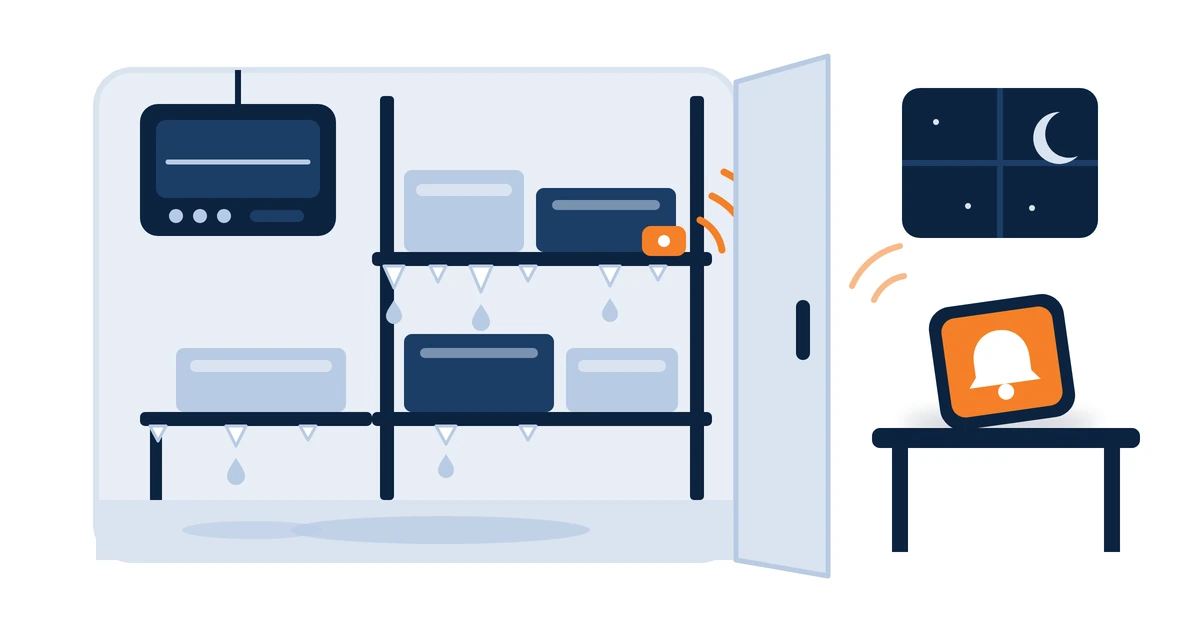
The fix is not complicated. Put a separate temperature sensor in each cold space that matters, reporting over its own connection to its own platform, with its own alert rules and its own logins. It should not talk to the refrigeration controller, and it should not be possible to change it through the controller.
What that gives you:
- A second opinion. If the controller says −20°C and the independent sensor says −8°C, the mismatch itself is the alarm.
- An alert path the attacker has not touched. Out-of-range readings go to a named person’s phone, whatever the controller is doing.
- A record you can rely on afterwards. When an insurer, customer or environmental health officer asks what the product experienced, you have a time-stamped trace that did not come from the compromised system.
What it does not do is just as important. It does not stop the attack, and it is itself a connected system, so ask its supplier the same security questions you would ask of anything else: how it is updated, how access is controlled, and how vulnerabilities are reported. Our own answers to those questions are in our Trust Center.
Why the stakes are high
The law sets the floor. Food hygiene law (Regulation (EC) No 852/2004, Annex II, as it applies in Great Britain) says: “The cold chain is not to be interrupted,” while allowing limited periods outside temperature control where that does not result in a risk to health. Government business guidance says chilled food must be kept at 8°C or below, which it describes as a legal requirement in England, Wales and Northern Ireland and a recommendation in Scotland. The same guidance recommends setting fridges to 5°C or below so that food stays cold enough even if the temperature changes.
The national picture raises the stakes further. In September the National Audit Office reported that around 50% of food for consumption in the UK goes through the cold chain, and listed “exposure to cyber incidents affecting temperature-control, monitoring and logistics systems” among the key risks facing it.
What to do this week
| Action | Source of the advice |
|---|---|
| Find out whether any refrigeration controller can be reached from the internet. Do not assume it cannot. | NCSC (August 2026): organizations “should not assume that their OT is inaccessible from the internet without verifying it” |
| Remove public internet exposure, and restore remote access only through a secure VPN or protected network | CERT-FR alert, 12 October 2026 |
| Before you cut the data link to your refrigeration contractor, check your insurance terms | CERT-FR alert, 12 October 2026 |
| Check the whole controller configuration, especially defrost schedules | CERT-FR alert, 12 October 2026 |
| Change default passwords, update firmware, and retire devices the maker no longer supports | CISA and partners, 5 November 2026 |
| Set reasonable setpoint limits and alerting for deviations | CISA and partners, 5 November 2026 |
| Fit an independent sensor in every cold room and vehicle compartment that matters, alerting a named on-call person | Our recommendation |
| Agree who goes to site at 2 a.m., and how they get in | Our recommendation |
The last row is the one most plans skip. An alert is only as good as the person who receives it and the action they can take. Decide in advance who carries the phone, what they do first, and when product is moved or held.
Vans, trailers and cold stores together
For operators running both buildings and vehicles, one independent sensor estate across cold rooms, fridge vans and refrigerated trailers keeps the alerting and the records in one place. Wireless sensors can be fitted without wiring into the refrigeration unit, which also suits rented and third-party trailers. If your tracking also reads the fridge unit’s own data, that is useful, but it is a second view of the controller, not an independent record.
You can see how the sensors, gateways and alerts fit together on our temperature monitoring page. For the wider picture in chilled distribution, see the food and beverage sector overview.
Sources: CERT-FR — Alert CERTFR-2026-ALE-012 (12 October 2026, updated 16 October 2026); ENISA, European Commission and Europol — Joint statement on cyber incidents in refrigeration systems across the EU (4 November 2026); CISA, FBI, HHS, USDA and DOT — US Government Partners Urge Hardening Industrial Refrigeration and Cold Chain Monitoring Systems (5 November 2026); NCSC — Richard Horne’s speech at the NCSC Annual Review 2026 launch (3 November 2026); NCSC — Disruptive cyber activity highlights risk from internet-exposed systems and edge devices (27 August 2026); The Record — British businesses caught in Europe-wide supermarket fridge attacks (3 November 2026); National Audit Office — Resilience of the food supply chain to disruptions (4 September 2026); Regulation (EC) No 852/2004, Annex II (legislation.gov.uk); GOV.UK — Food hygiene for your business: chilling and freezing. Every source checked again on 15 November 2026. General guidance, not legal advice.